


BiblioTech
CTech's Book Review: You cannot defend what you cannot see or understand
Moshe Ben Simon, CPO at Axonius, shares insights after reading “Sandworm: A New Era of Cyberwar and the Hunt for the Kremlin's Most Dangerous Hackers”, by Andy Greenberg.
Moshe Ben Simon, CPO at Axonius, an asset intelligence platform. He has joined Ctech to share a review of “Sandworm: A New Era of Cyberwar and the Hunt for the Kremlin's Most Dangerous Hackers”, by Andy Greenberg.
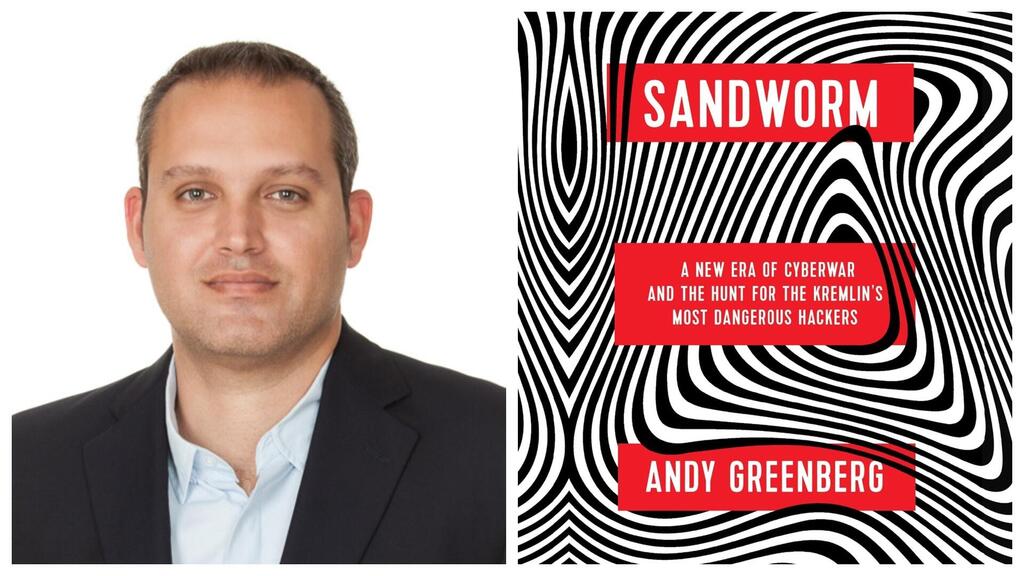
Title: Sandworm: A New Era of Cyberwar and the Hunt for the Kremlin's Most Dangerous Hackers
Author: Andy Greenberg
Format: Tablet
Where: Commute
Summary:
Sandworm by Andy Greenberg chronicles the rise of Russia's most destructive state-sponsored hacking group (GRU Unit 74455, also known as “Sandworm”) and the birth of a new era in digital warfare. The book traces a devastating sequence of attacks, including blackouts in Ukraine caused by power grid hacks and the deployment of NotPetya (the most destructive malware in history with more than $10 billion in damages).
Greenberg details how state-sponsored cyber warfare transitioned from silent espionage to indiscriminate, physical-world sabotage. By following security researchers and intelligence operatives racing to identify the threat actor behind these attacks, the book exposes the severe fragility of global digital infrastructure and shows how nation-state threat actors weaponize supply chains to inflict billions of dollars in collateral damage on companies worldwide.
Important Themes:
One of the central themes of Sandworm is a shift in cyber warfare from silent espionage to indiscriminate, physical-world sabotage. Greenberg illustrates how cyber weapons have crossed the boundary from the digital realm into critical infrastructure. When nation-states target power grids and hospital networks, along with the shipping lanes that keep global trade moving, digital security stops being an IT department concern and becomes a matter of organizational survival and national resilience.
Another prominent theme is systemic interconnectedness and the inevitability of collateral damage. The story of NotPetya demonstrates that modern enterprise environments are so tightly linked that a single attack can paralyze global supply chains within hours. The attack did not discriminate between its intended targets and multinational corporations that had nothing to do with the conflict. In a hyper-connected ecosystem, an attack on one company can shut down others that were never the target.
Finally, the book examines the lethal danger of organizational blind spots and unmanaged assets. GRU Unit 74455 rarely needed exotic zero-days. Its attacks combined missing visibility and unpatched systems with, in NotPetya's case, a trusted software update turned into a backdoor. The book shows that legacy perimeter defense is obsolete once threat actors can move laterally through legitimate access points and infrastructure links that no one mapped.
What I’ve Learned:
Reading Sandworm reinforces a foundational truth in cybersecurity: you cannot defend what you cannot see or understand. In product development, we often focus on building static inventories and periodic scans, but Greenberg's account illustrates that the most destructive attacks exploit basic visibility gaps and uncontrolled digital assets. NotPetya crippled multinational giants that had plenty of sophisticated security tools. What they lacked was a unified, real-time understanding of the devices, applications, and dependencies inside their own attack surface.
This book deeply influenced my perspective on product strategy and asset intelligence. It proved that defenses cannot rely on static boundaries or isolated security silos. When threat actors operate with nation-state resources and target supply chains, security teams need continuous, comprehensive context over their entire environment. Designing products that provide complete operational clarity, while eliminating blind spots before a threat actor can find them, is the baseline requirement for modern cyber defense. But visibility alone doesn't close the gap. It must translate into prioritized, coordinated remediation across security and IT teams.
Sandworm also taught me that resilience must be built into the DNA of digital architecture. As products become more interconnected, product leaders must design systems that assume breach and give organizations the ability to find new assets and act on them instantly. Security is about giving organizations the visibility and control to withstand threats they can't fully predict.
Critiques:
While Sandworm reads like an edge-of-your-seat thriller, its primary focus is investigative journalism and political context rather than granular technical forensics. Security engineers looking for deep code-level analysis or defensive implementation blueprints won't find them here.
However, this high-level narrative structure is precisely what makes the book so valuable. It elevates cyber risk to a strategic, board-level conversation rather than keeping it buried in technical jargon.
Who Should Read This Book:
I recommend Sandworm to CISOs, CIOs, CPOs, technology executives, and any business leader who needs to understand the real-world scale of modern cyber threats. You don't need a deep technical background to appreciate it. If you want to understand how nation-state threat actors operate, why traditional perimeter security is no longer sufficient, and why total visibility across your digital footprint is essential to enterprise survival, Greenberg provides an indispensable blueprint.