


The French refrigerator hack was not sophisticated. That’s what makes it frightening
Hackers exploited outdated software, weak login protections and internet-exposed systems to overheat refrigerators at hundreds of supermarkets. The incident highlights a longstanding IoT security problem with consequences that can extend well beyond food waste.
Aside from the scale of the damage, this week’s cyberattack on supermarket refrigeration systems in France was not unusual, either in its sophistication or in the weak defenses that made it possible. And that is what makes it so frightening.
On Monday, it emerged that hackers had breached the systems controlling refrigerators at hundreds of locations across France overnight, forcing temperatures up to 50 degrees Celsius and causing fires and extensive food losses. The Paris prosecutor’s office described it as a “large-scale” attack affecting “network-connected refrigerators at several of the largest food chains in France.”
Les Mousquetaires, which owns the Intermarché chain, initially reported that about 150 of its stores had been affected. All the food in the affected refrigerators was discarded to avoid health risks. Dominique Schelcher, CEO of Coopérative U, also confirmed that the chain had been hit. Carrefour said 80 of its supermarkets were affected, a small fraction of its network of approximately 6,000 stores.
1 View gallery
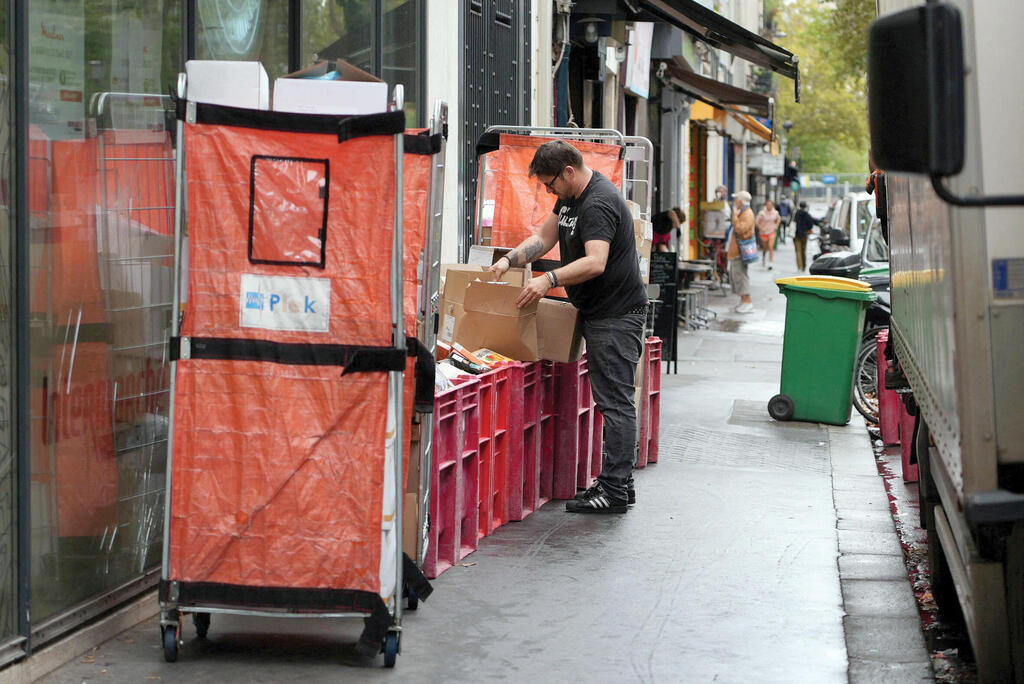
A worker throws away food at an Intermarché branch. They didn’t take any chances.
(Photo: Lucien Libert/Reuters)
The incident attracted worldwide attention because of its unusual target and visible consequences. Technically, however, it was a familiar kind of attack. Breaches involving smart products, or Internet of Things (IoT) devices, are routine. These devices include household appliances, security cameras, televisions and routers. They often operate in the background and are not necessarily viewed by users as gateways to sensitive personal information.
Yet their security protections are often weaker than those of smartphones and computers. Their operating software may go unpatched for long periods, even when manufacturers release updates. Basic safeguards are frequently missing, and many users never change default usernames and passwords. As a result, specialized search engines such as Shodan can identify internet-connected devices that are exposed or poorly protected, making them easier for attackers to find and target without advanced technical skills.
The French refrigerator attack illustrates several of these failures. The affected refrigeration controllers, manufactured by Denmark’s Danfoss, were running outdated software containing vulnerabilities that could allow attackers to execute commands remotely, take control of the controllers or disable temperature-change alerts.
The attackers also exploited default login credentials. The username was always “admin,” while the password changed daily but was effectively the date. Another vulnerability allowed the attackers to reset login settings to their defaults, even if operators had previously changed them. Many of the refrigerators were also exposed through Shodan or similar services.
The refrigerators are simply the latest example of a problem security experts have warned about for years. Estimates put the number of IoT devices worldwide at more than 20 billion, excluding computers, smartphones, tablets and similar devices. Many could provide an entry point for attackers if they are not properly secured. Unprotected security cameras, for example, became a significant concern during the war with Iran, when Iranian hackers accessed cameras in Israel.
The success of the French attack could encourage others to attempt similar operations. The next time, the consequences could extend far beyond spoiled food.