



Security Researchers: Digital Fighters Series
AI is transforming the hunt for vulnerabilities as the attack surface grows
CTech’s “Security Researchers: Digital Fighters” series surveyed 30 security researchers from Startup Nation’s cyber landscape, revealing how AI is compressing the time and cost of security research but expanding the attack surface.
“Attackers are already using AI to automate, within minutes, attacks that once required nation-state-level resources and technical expertise available only to the most sophisticated organizations," warned Avital Leshem, Group Manager of Exposure Management at Check Point.
Within Israel’s cyber companies are small, highly specialized teams trained to think like attackers, find vulnerabilities and stay ahead of a threat landscape increasingly accelerated by AI. CTech’s Security Researchers: Digital Fighters Series” series surveyed 30 of these security research professionals.
5 View gallery
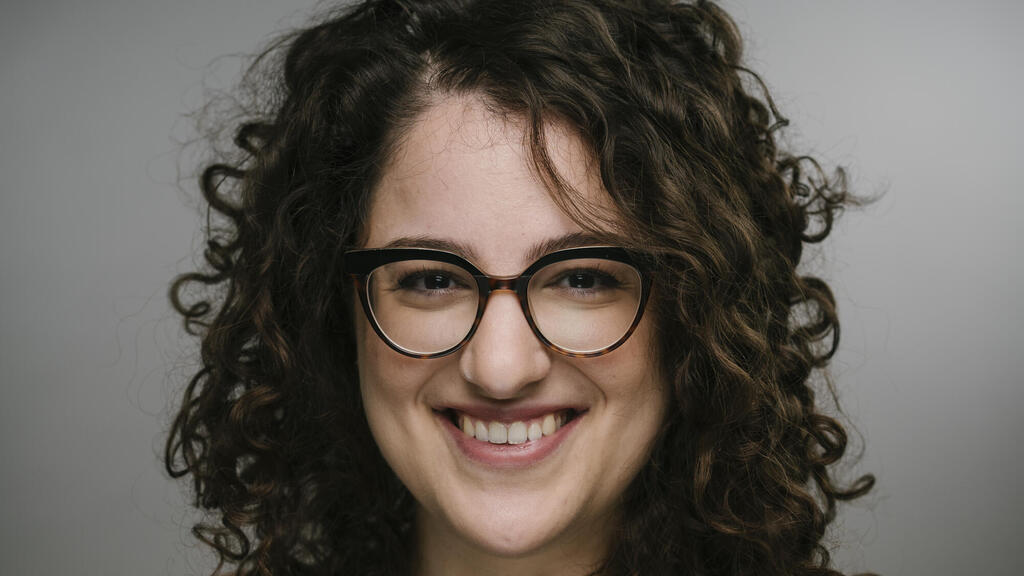
Avital Leshem, Group Manager of Exposure Management, Check Point.
(Photo: Maxim Dinshtein)
The responses were illustrative of the rapidly developing threat and architectural landscape in cyberspace: the collapsing time and cost and resources required both to discover and exploit vulnerabilities, how threat actors are weaponizing and exploiting AI architectures, and ultimately, how the industry is repositioning its research to meet the renewed demands of the threat environment.
The democratization of asymmetric threats
Attack capabilities once thought to be uniquely the preserve of nation-state units are now accessible to the masses, off the shelf. By the same token, the time and resources for security teams to find these vulnerabilities have also collapsed. In fact, nearly a third of the companies surveyed emphasized that commercial AI tools have condensed these timelines.
“Historically, the primary bottleneck for researchers was implementation – turning a theoretical concept into a functional Proof of Concept (PoC) to test a hypothesis often took months,” said Shoham Danino, Senior Researcher at Surf AI. “Today, with AI, we achieve that in a matter of days.”
Across the survey, five companies specifically highlighted small teams or a single researcher finding zero-day flaws in popular commercial software, including Zoom, Google Cloud, and Microsoft Copilot.
For example, Alex Mor, Security Research Manager at A Security, recalled a zero-day flaw a team member uncovered in Zoom. “Building an attack like that against closed commercial software used to take a government, a team of experts, and months of work,” warned Mor. “The story is that this took one researcher one day, using AI models anyone can pay for.”
Security research is having its “AFL fuzzing moment”
“AI made it cheap to produce an answer and expensive to trust one,” stated Idan Revivo, Head of Security Research at Island. In the survey, a fifth of the companies noted that while AI excels at detecting surface-level vulnerabilities, its tendencies to hallucinate, lose context, or generate false confidence has made the discerning of truth all the more valuable a skill to the discipline of security research.
“AI is having its AFL moment,” described Uri Katz, Director of Research at Oligo Security, referring to the automated fuzzing revolution that took place after the tool was released in late 2013. “Right now you can throw AI at a project and it'll find the low-hanging fruit, but that basic attack surface will eventually get covered, the same way it did with fuzzing.”
Needless to say, the vast majority of respondents stressed just how irreplaceable independent human judgment remains to the field.
“They can find things that would take a human researcher significant time to discover, but they also fabricate findings, lose context as the story unfolds, and sometimes pursue the wrong hypothesis for too long,” noted Mor.
Context manipulation is the new password theft
“The attacker does not necessarily need your credentials,” explained Sasi Levi, Security Research Lead at Noma Security. “Sometimes they only need influence over something your trusted agent will consume.” Indeed, a fifth of companies noted that enterprise risk is moving away from user credentials and toward manipulating trusted AI agent permissions.
“The threat AI creates is not about what AI models say, but about what agents do,” said Tamir Ishay Sharbat, Director of Security Research at Zenity, whose team demonstrated a industry foundational indirect prompt injection attack that impacts real-world environments through Microsoft Copilot at Black Hat USA 2024. “Simply sending an email, an attacker can hijack Microsoft Copilot to give misleading answers, phish the victim... and harvest sensitive data."
“The threat AI creates is not about what AI models say, but about what agents do,” said Tamir Ishay Sharbat, Director of Security Research at Zenity, whose team demonstrated the industry's first indirect prompt injection attack that impacts real-world environments through Microsoft Copilot at Black Hat USA 2024. “Simply sending an email, an attacker can hijack Microsoft Copilot to give misleading answers, phish the victim... and harvest sensitive data.”
Zenity was one of four companies that published original research demonstrating zero-click exfiltration or takeover via AI agents consuming shared documents, emails, or web pages.
In another example, Omer Nissim, Security Researcher at Sweet Security, described how an internal AI assistant was exploited to bypass a company's perimeter: “The target's own AI handed over the one piece of information standing between the outside world and the whole environment,” Nissim recalled.
AI costs are turning into an attack vector
As Security Operations Centers (SOCs) increasingly rely on AI models to automatically process security alerts, threat actors have discovered a way to exploit the cost structure in an act of economic warfare.
“Every alert that arrives is read, enriched and reasoned about by a model before a person ever sees it, and each of those steps costs tokens,” explained Ido Shtrauch, Security Research Team Lead at Conifers AI.
Three of the survey respondents flagged the growing trend of economic attack vectors where adversaries flood automated SOC engines with noise in an effort to exhaust an enterprise's AI token budgets.
“Much of the volume was not hiding anything at all,” Shtrauch continued. “Analyzing it costs us every single time. Send tens of thousands and the company has spent its AI budget on garbage... Sometimes it is the weapon.”
Vulnerability severity scores are becoming outdated
In the survey, over a quarter of the companies rejected isolated vulnerability severity scores (CVEs), advocating instead for broader, big-picture thinking to realistically assess contextual risk and network reachability. "Our ‘Moby Dick’ is the attack chain that no one sees because none of its links look dangerous on their own: a medium-severity vulnerability, a minor misconfiguration, a gap in a security control that never raises an alarm," said Amir Shavitt, Head of Research at Zafran.
Overall, five companies detailed how connecting a series of minor or low-severity flaws could ultimately result in full administrative compromise, effectively handing the keys to the attacker.
“My ‘Moby Dick’ is the moment when the industry will finally understand that a vulnerability does not exist on a server alone,” Yuval Barak, Founding Research Engineer at Astelia, similarly expressed. “It exists inside a network, behind controls, and along a path an attacker may or may not be able to take."
AI infrastructure blind spots
Many respondents noted how external platforms have become a major blind spot in the enterprise perimeter, with attackers increasingly targeting trusted third-party dependencies. Nearly a third of the companies identified open-source AI infrastructure (such as Ollama and MCP bridges), code platforms like GitHub, and browser extensions as growing grounds for risk.
"GitHub is where a large share of supply chain attacks actually begin, yet almost nobody monitors it,” stressed Mor Weinberger, Security Researcher at Echo. “Companies run EDR on their endpoints and monitoring across their cloud, and the platform their code comes from stays a blind spot."
Among respondents, five had uncovered critical flaws in widely used AI tools, dependencies, or browser extensions. "MCP servers, agent skills and plugins are being adopted quickly, often in ecosystems with limited history to help establish trust,” said Revivo. “My ‘white whale’ is the malicious dependency that has earned its place in the workflow.”